A database per company
Multi-tenant usually means your rows sitting beside someone else's behind a filter. HisabNest provisions a separate database for each company, so one tenant's query cannot reach another's ledger even if the filter were wrong.
Security
Financial records deserve stronger guarantees than a privacy page full of adjectives. Here is specifically how HisabNest separates, protects and hands back your data.
Multi-tenant usually means your rows sitting beside someone else's behind a filter. HisabNest provisions a separate database for each company, so one tenant's query cannot reach another's ledger even if the filter were wrong.
Admin, Sales, Inventory and Accounts roles map to a permission matrix you can edit per company. Sensitive actions — voiding an invoice, overriding a credit limit, viewing margins — are separate permissions rather than implied by seniority.
User passwords are stored as bcrypt hashes, never in plain text. Integration secrets — your SMTP password, your WhatsApp access token — are write-only: the settings screen shows whether one is set, never the value itself.
Invoices, cancellations, stock adjustments, permission edits and logins are written to an append-only audit log with the user, timestamp and reference, so a disputed entry has a history rather than an argument.
Any admin can pull a complete JSON export of every record — masters, documents, ledgers, journals, payroll — at any time, on any plan. No support ticket, no exit fee, no 'contact your account manager'.
Bearer tokens are cryptographically random, bound server-side to the identity they were issued for, and expire after twelve hours. Repeated failed logins lock the attempt window rather than inviting a guessing game.
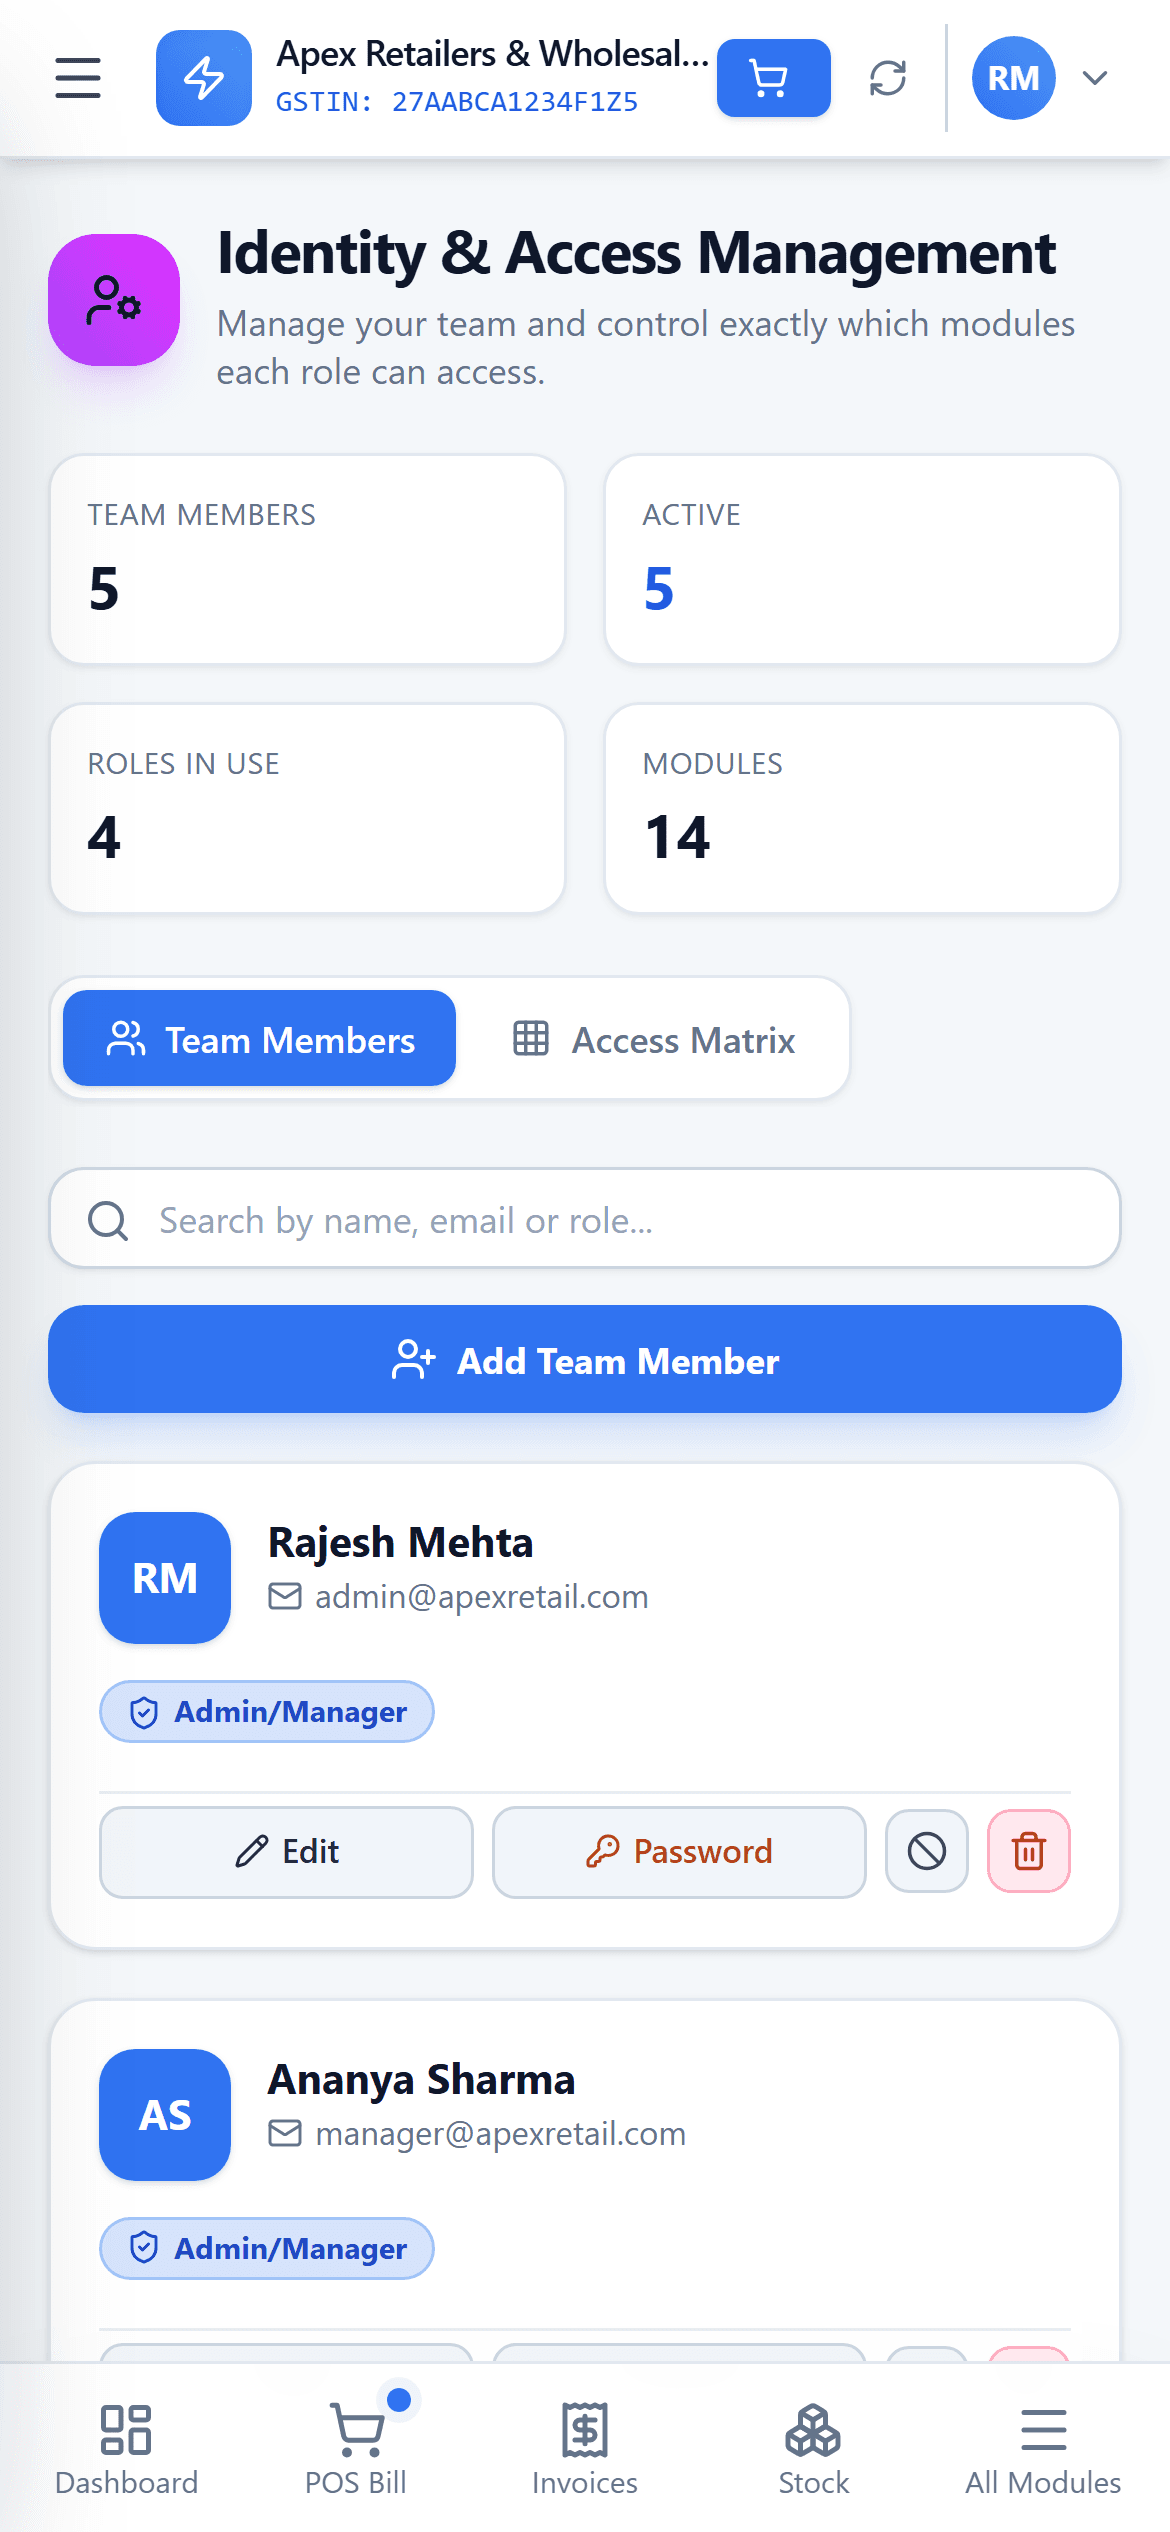
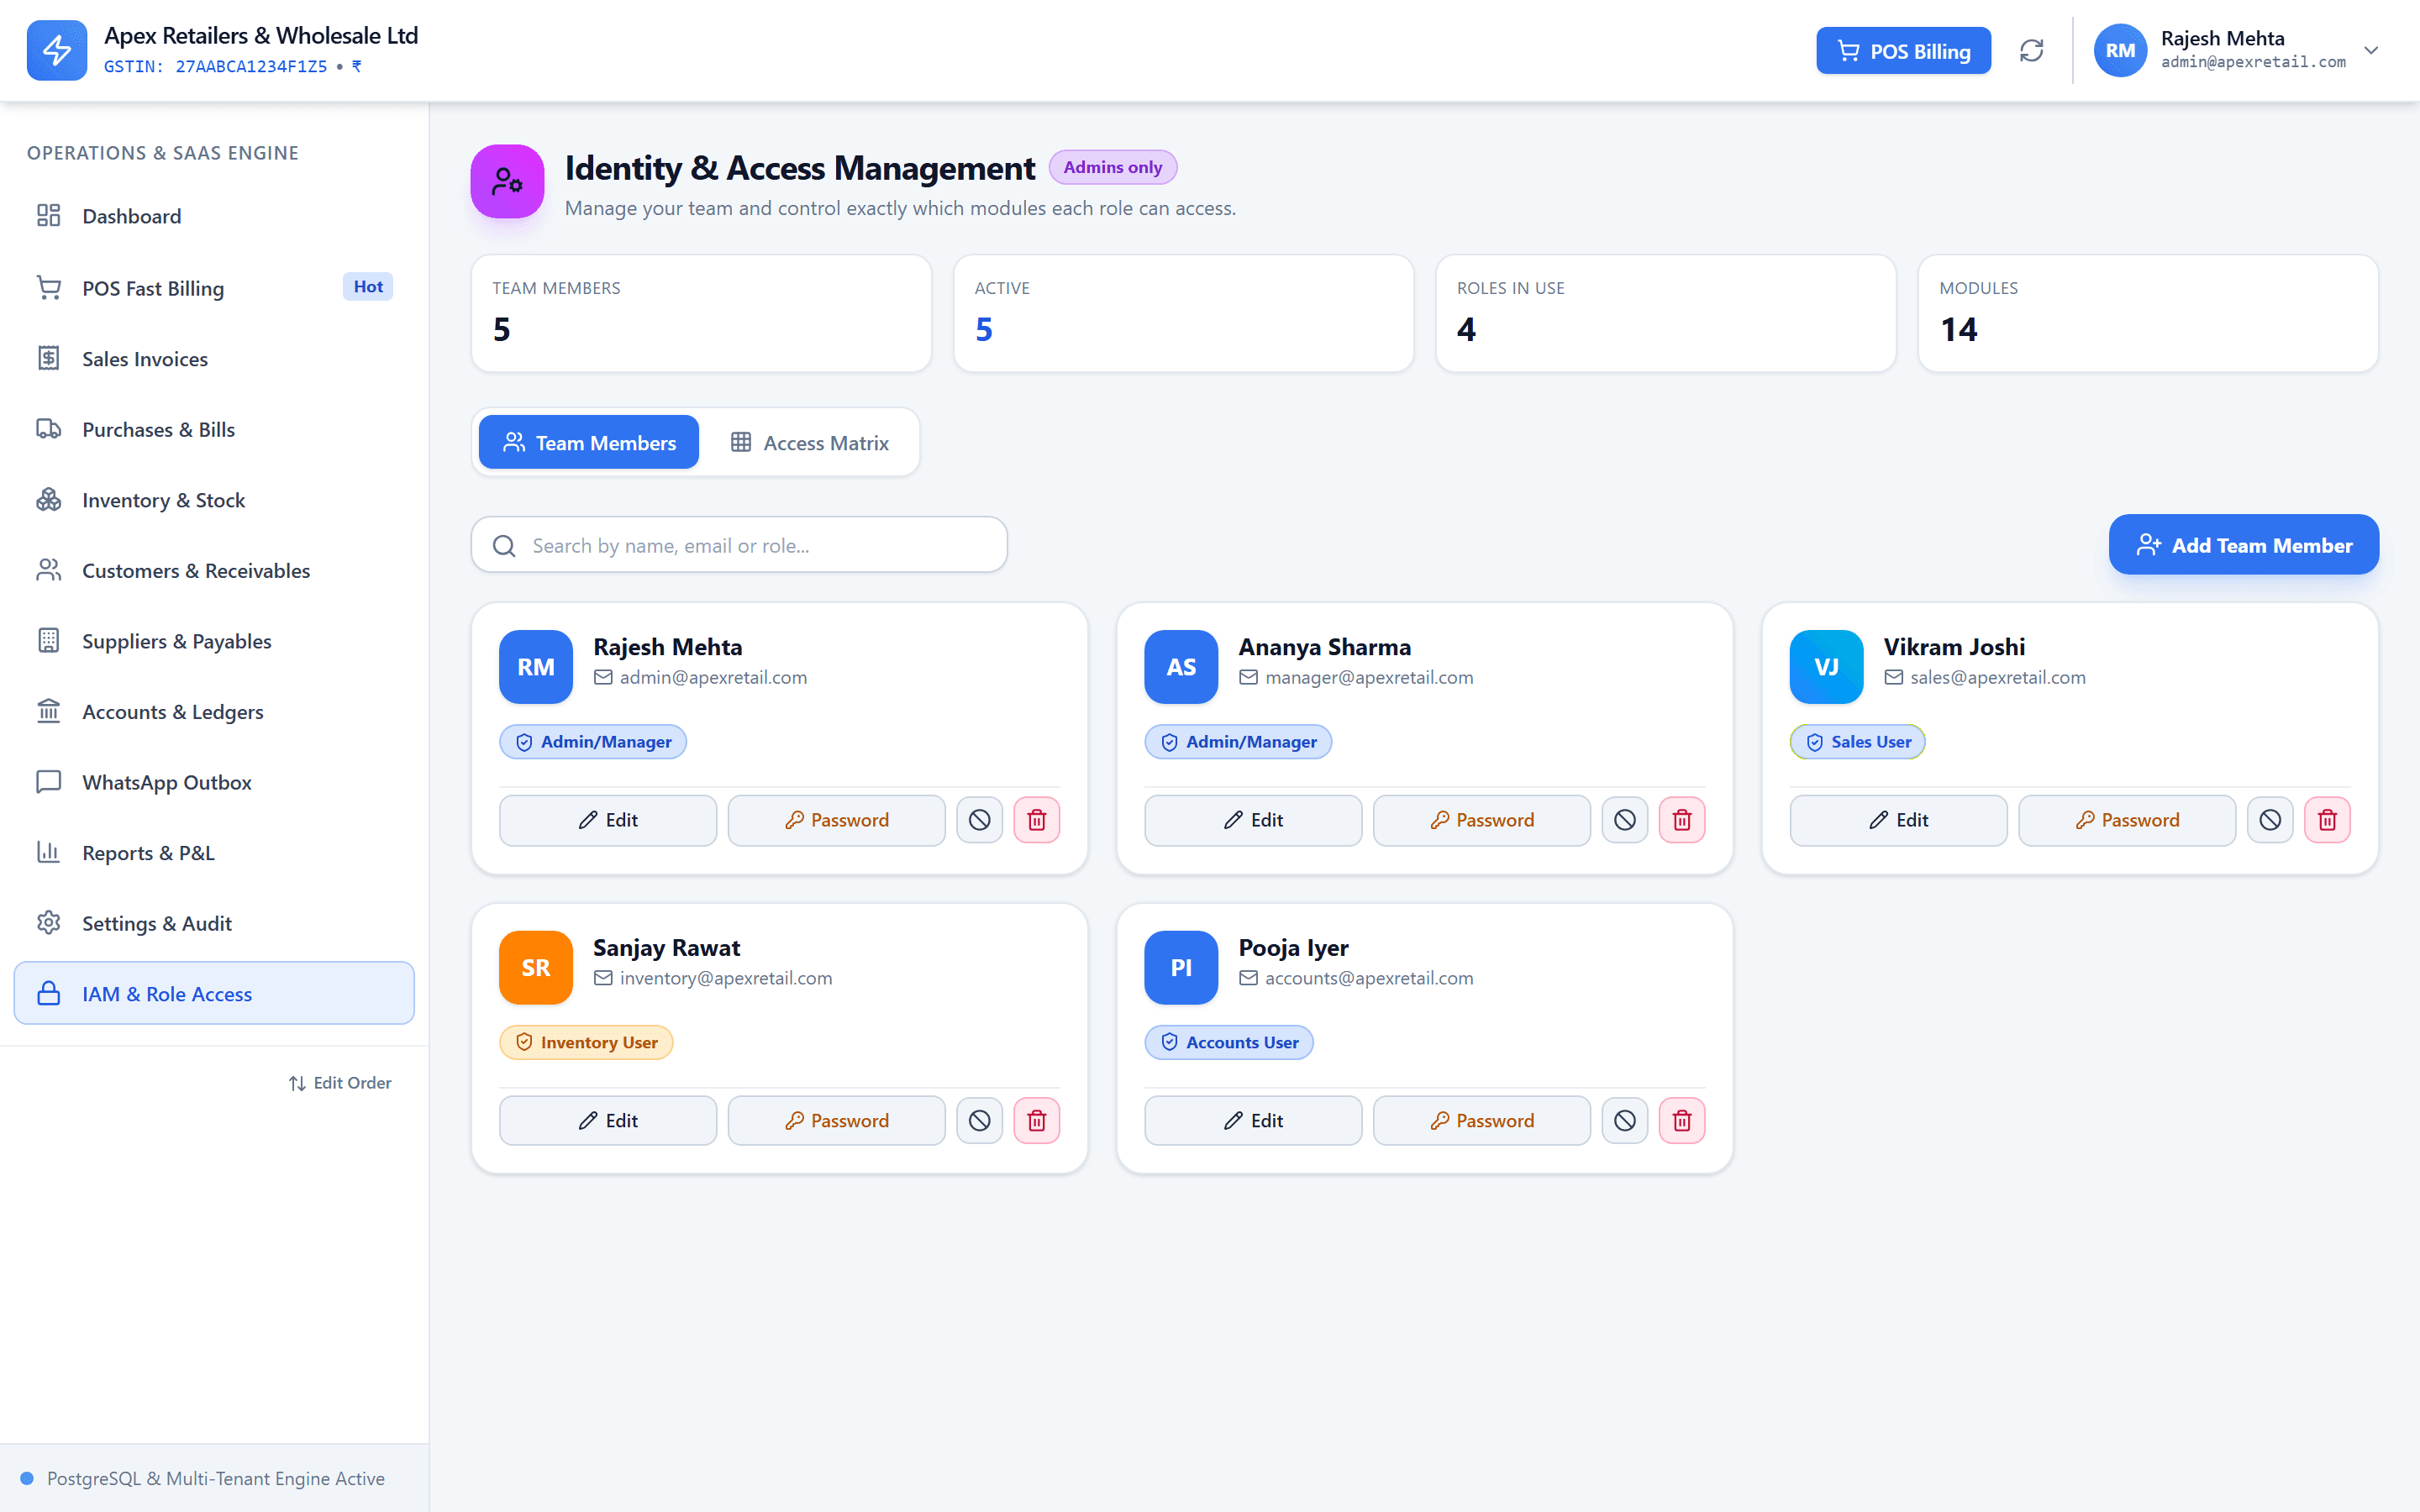
Role-based access, edited per company. Every toggle here is enforced on the server, not merely hidden in the interface.
On infrastructure hosted in India, in a PostgreSQL database provisioned per company, with encrypted connections in transit.
Your team sees exactly what their roles allow. HisabNest staff open a workspace only to help with a support request, and anything they change is recorded in your audit trail as HisabNest Support.
It is stored against your company only, used solely to call Meta's API as your own business number, and never returned to any client — including your own browser.
Never. HisabNest prepares return data for you or your CA to file. We are not a filing intermediary and have no reason to hold portal logins.
Your data is never deleted automatically when a subscription lapses, and any admin can download a complete JSON export of every record at any time — so leaving never means losing your books.
Yes — it is part of the standard JSON export, and your own admins can review it on screen at any time under Settings & Audit.
We're happy to walk an internal reviewer or auditor through the isolation model, permission matrix and audit trail before you commit.